CRM for cybersecurity consultants

CRM for Cybersecurity Consultants with a Scope Change Workflow

Cybersecurity consultants face operational drift when a security assessment adds a new system after authorization and scope are agreed. Workspace369 documents these changes in client records, Proposals, tasks and invoices. Your advisory firm tracks every scope update, schedule change and invoice for the engagement in one place.

Clientthe relationship and agreed brief
Worktasks with a responsible person
Billinginvoices and commercial context
Workspace369 client record showing history, files, communication, and invoices in one profile

Key facts

CRM for cybersecurity consultants at Workspace369 covers 9 areas, including client records, proposals, projects and tasks.

The workflow runs in 5 steps, from "documenting the initial authorization" to "executing the revised invoice".

Workspace369 starts at $29/mo for 1 seat, and the Commander plan includes 20 seats, 500 GB of storage, and 120,000 AI tokens per month at $299/mo.

Additional seats cost $10 each and 100 GB of additional storage costs $15; full pricing is public on the Workspace369 pricing page.

The problem

Operational Friction in Security Assessments

Unauthorized Scope Creep

When a security assessment adds a new system after authorization and scope are agreed, consultants often perform unbilled work. Without immediate updates to Proposals and client records, the technical team tests unauthorized infrastructure. This creates a disconnect between active projects and the original contract, forcing administrative staff to retroactively adjust scheduling and tasks without clear documentation.
Scattered Assessment Files

Consultants frequently separate project files from the core administrative record. When a client requests a scope extension for an unmapped network segment, the conversation remains trapped in email. Without linking these conversations and files to the primary client records, billing personnel cannot verify if the additional assessment hours match the modified project milestones or the final generated invoices.

Misaligned Project Scheduling

Adding a newly discovered server to an active penetration test disrupts existing engineer scheduling. If the client-work system cannot quickly update tasks and scheduling, consultants miss deadlines on adjacent projects. This operational breakdown occurs because the administrative team lacks visibility into the scope changes documented in the project files, causing delayed invoices and friction during client portal reviews.

Delayed Scope Invoicing

Billing for a security assessment adds a new system after authorization and scope are agreed, which complicates standard billing workflows. If invoices are generated from static templates rather than updated client records and revised Proposals, the extra technical work can go unbilled. Consultants must manually cross-reference project tasks and files to ensure the newly discovered systems are accurately reflected on client invoices for the assessment.

The product

See the workspace your clients feel.

01

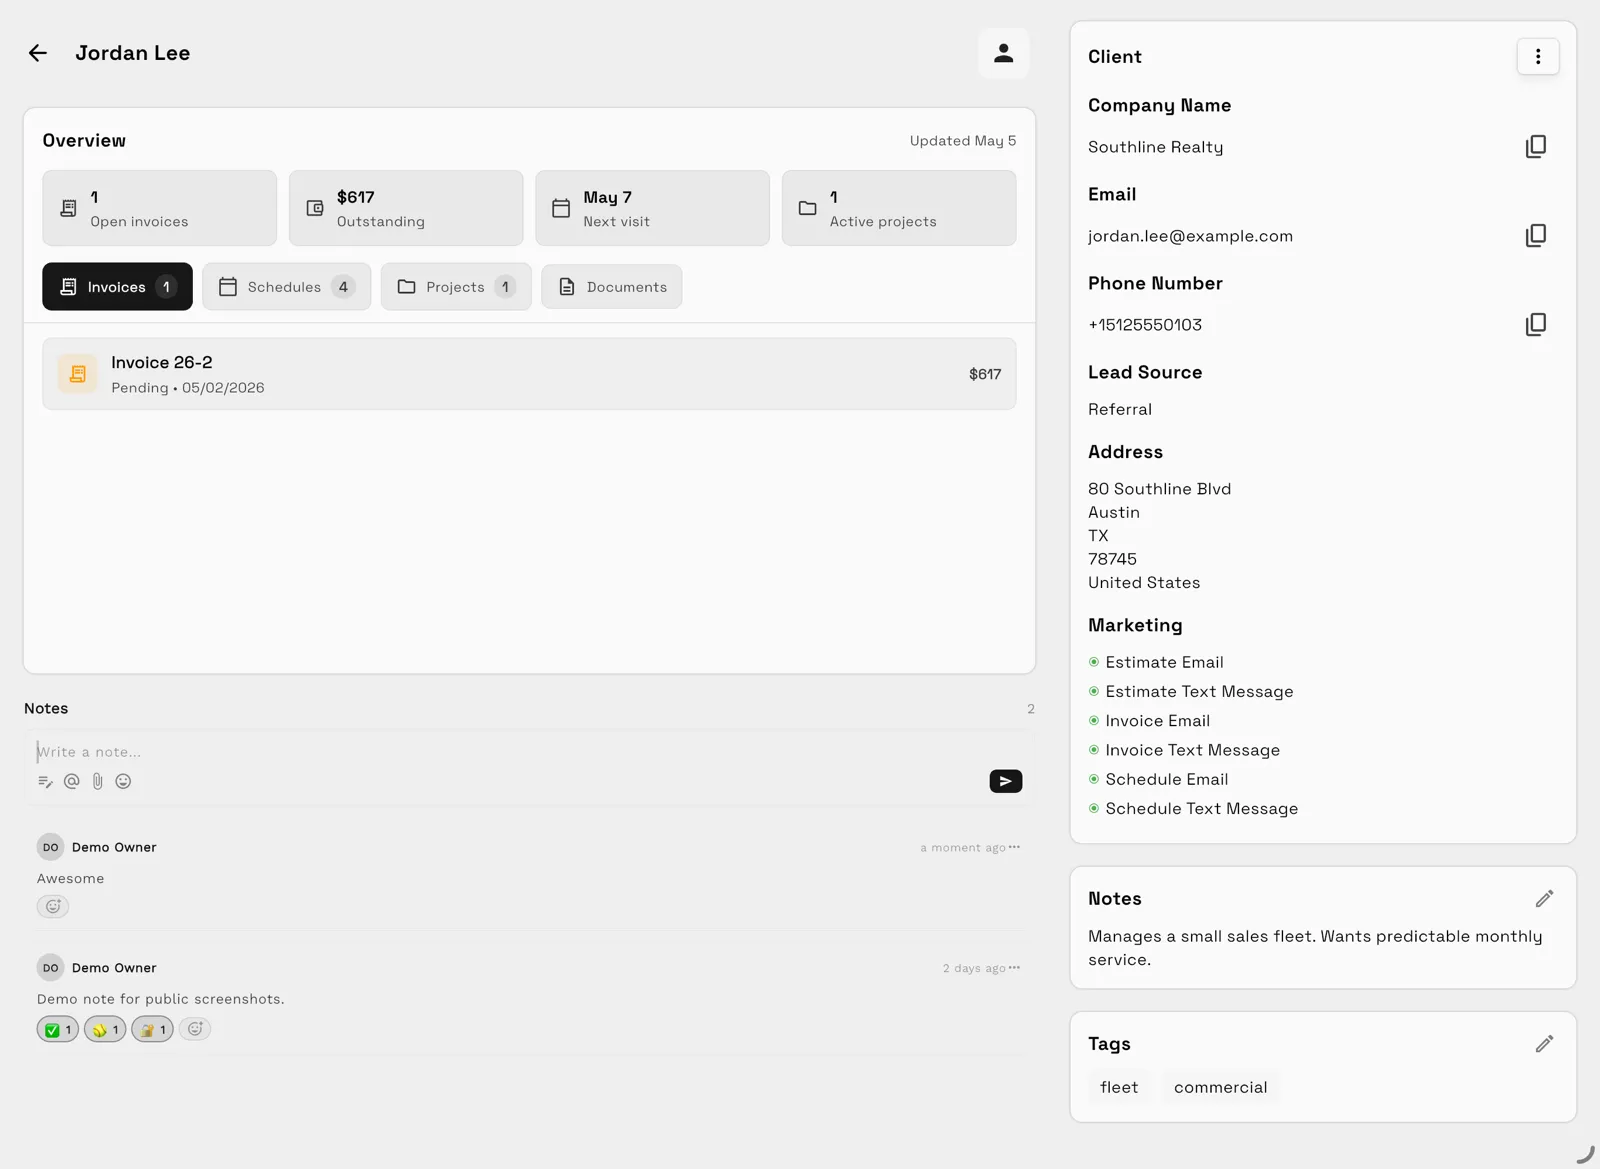
A portal clients actually check

Clients watch progress, files, and invoices in a branded portal instead of asking your team for updates.

Workspace369 client record showing history, files, communication, and invoices in one profile
02

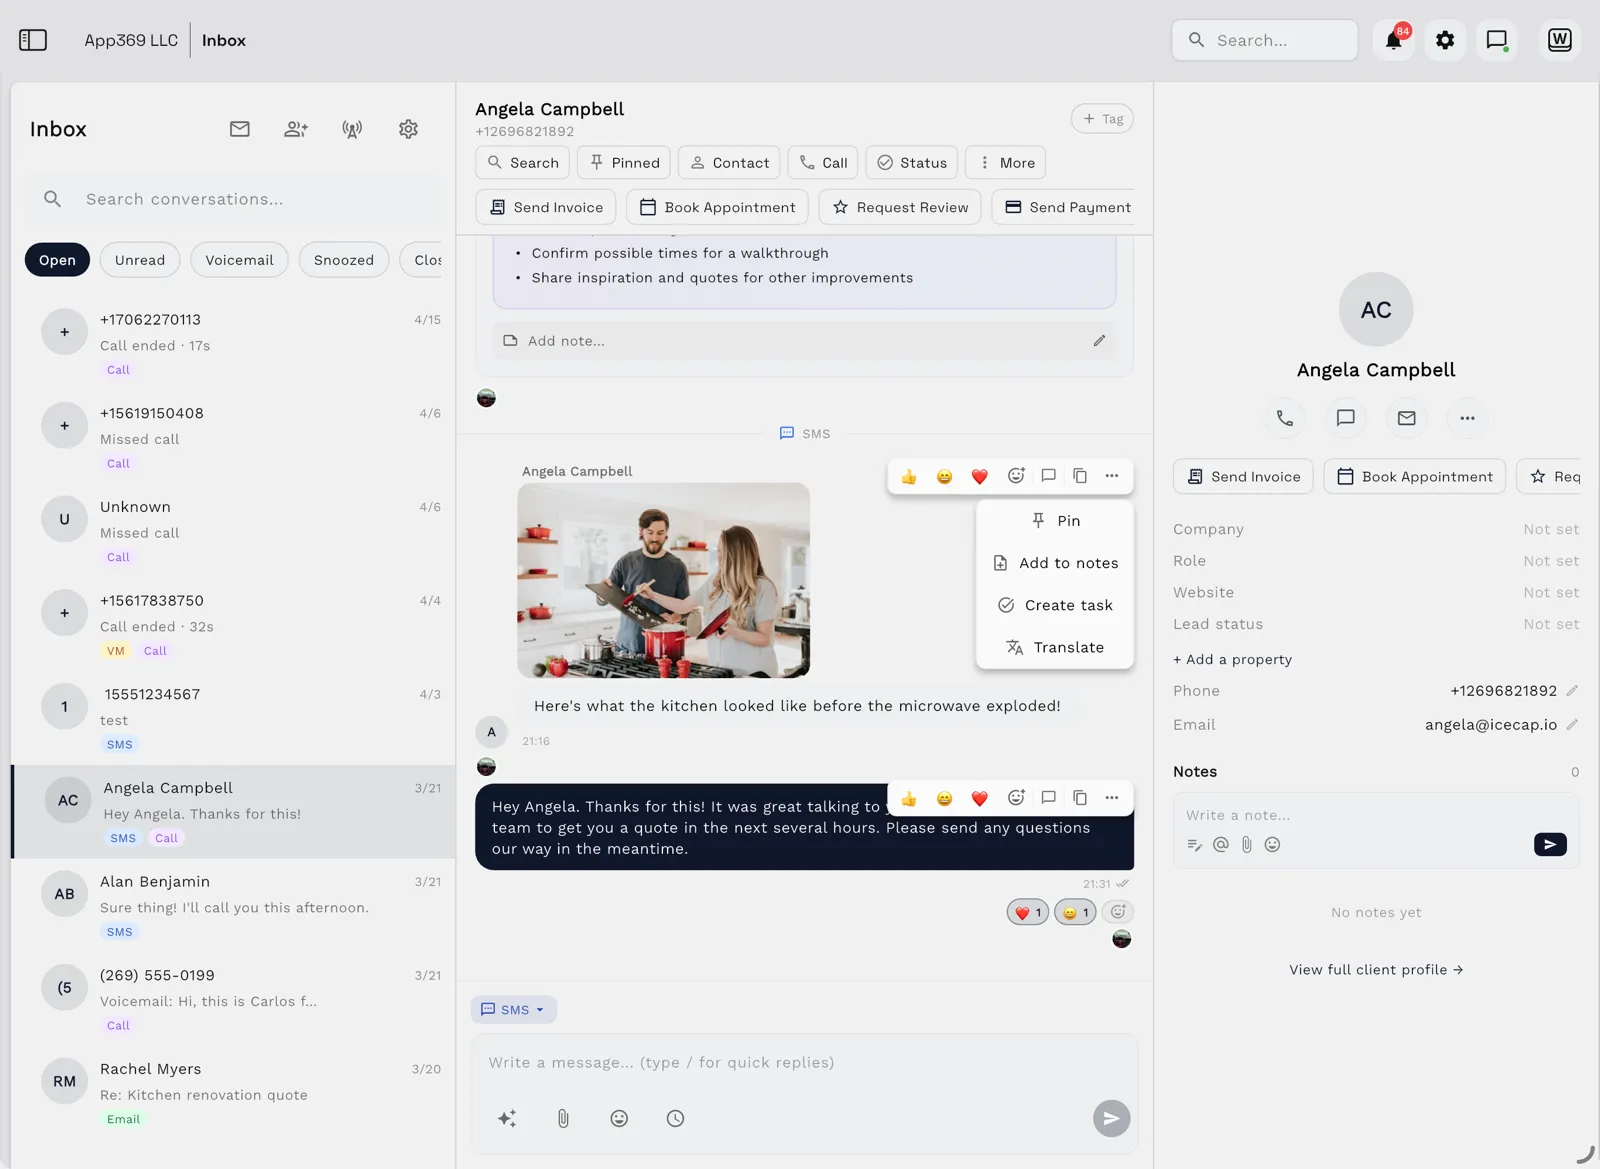
Every channel in one inbox

Email, SMS, calls, and voicemail land beside the client record — with AI summaries, so anyone on the team can reply with full context.

Workspace369 shared inbox showing email, SMS, and call history beside a client record
03

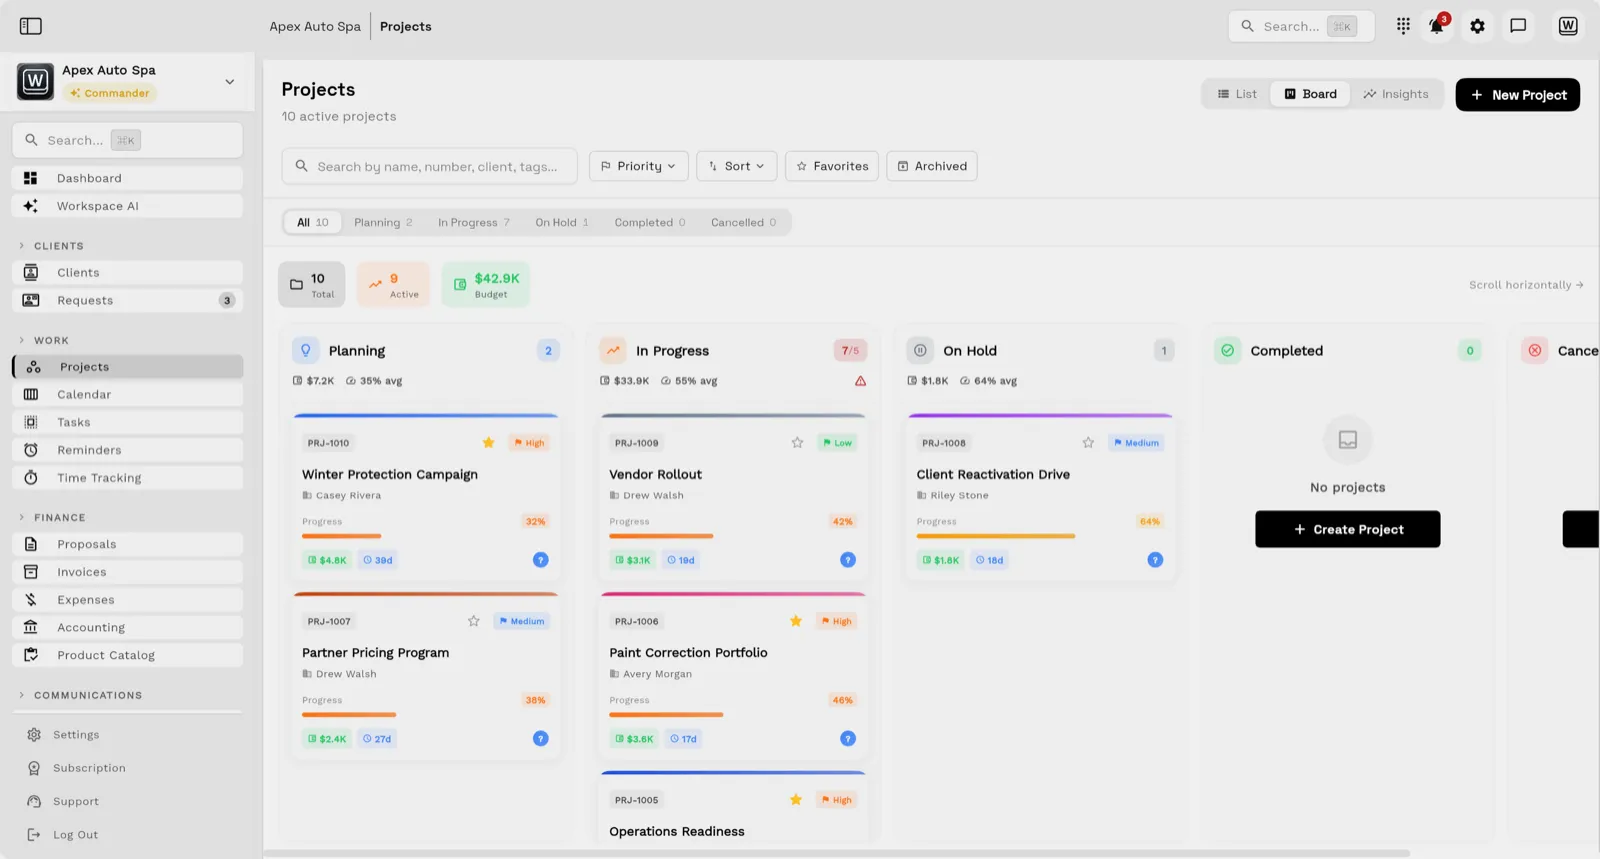
Client work, organized as projects

Tasks, files, and status for every engagement — visible to the team and, through the client portal, to the client.

Workspace369 project board showing client work organized into stages with owners and status
04

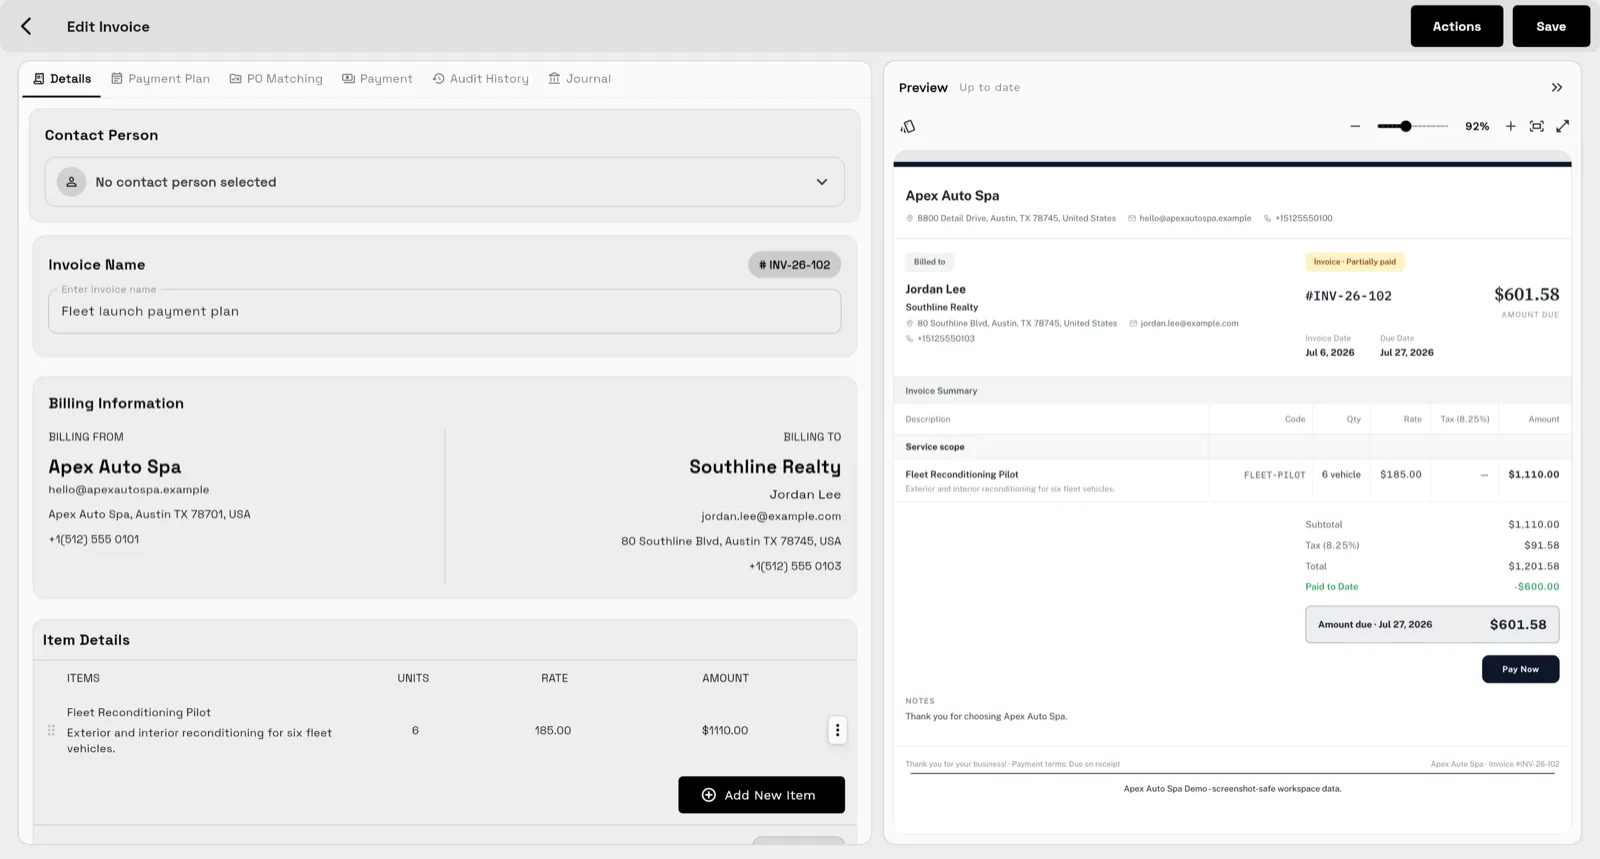
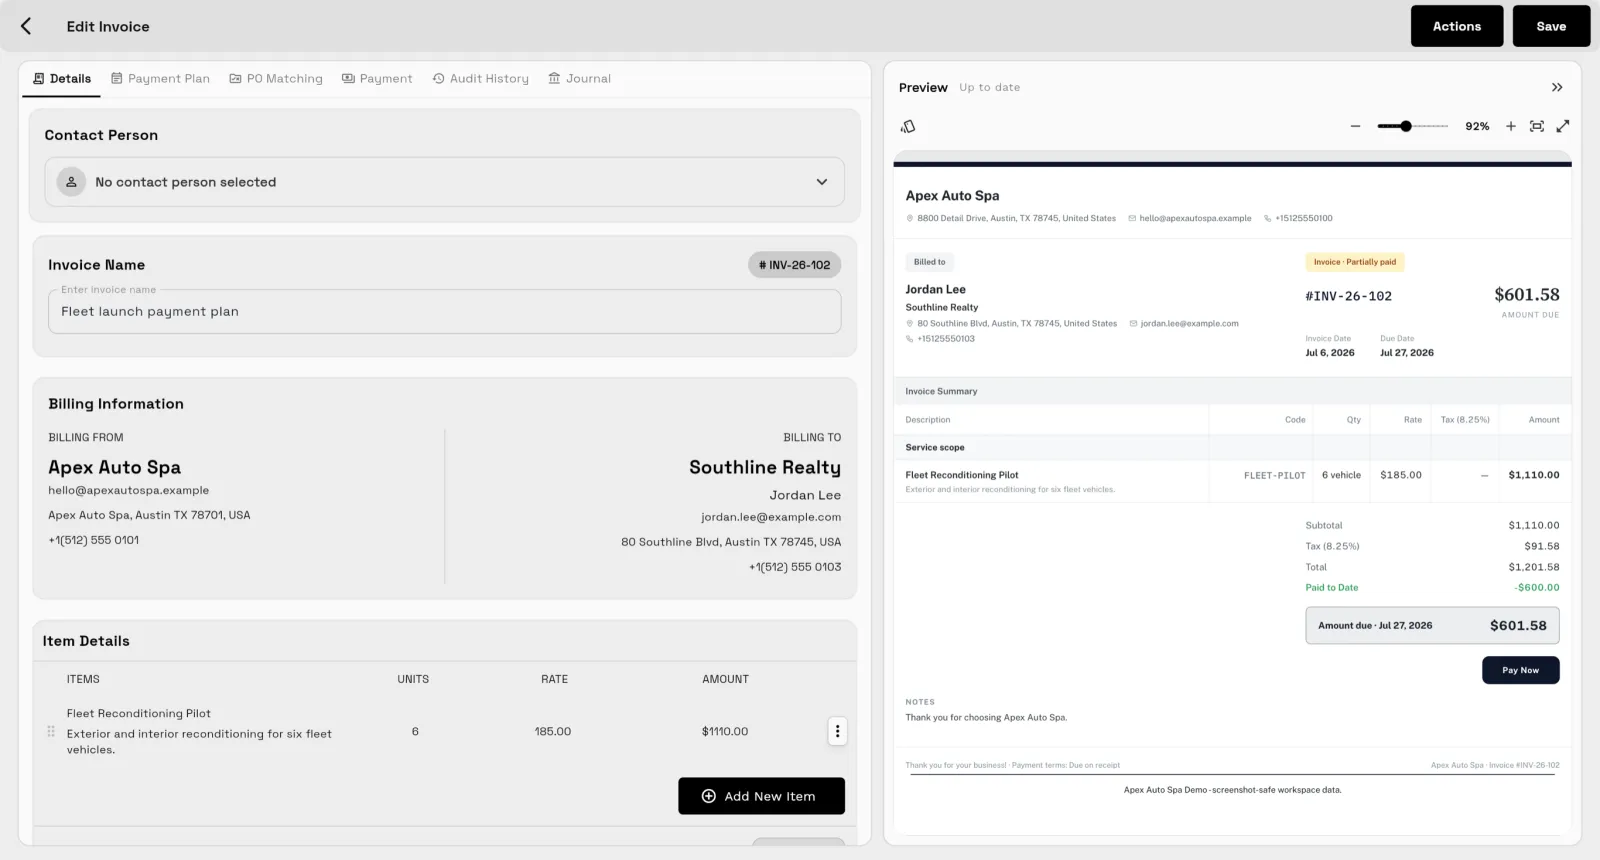
Proposals to paid invoices

Send quotes, bill milestones or retainers, and let automated reminders chase anything outstanding.

Workspace369 invoice editor showing line items, payment terms, and client details

Workflow

The Scope Change Management Workflow

01

Documenting the Initial Authorization

The workflow begins by establishing the baseline in client records and executing formal Proposals. Consultants schedule the initial assessment window using the scheduling tool and assign specific technical tasks to the security team. All initial project parameters, authorized IP ranges, and client conversations are anchored within the core system, providing a clear starting point before any active vulnerability scanning or technical field work commences.

02

Recording the Discovered Infrastructure

When a security assessment adds a new system after authorization and scope are agreed, the consultant must log this discovery. Instead of updating technical vulnerability scanners immediately, the operator records the scope change in the brief within the project files. The consultant initiates a new conversation with the client to flag the infrastructure expansion and request formal written confirmation.

03

Updating Proposals and Client Portal Access

Once the client agrees to the expanded testing boundary, the consultant issues an updated proposal. This updated document details the additional tasks and adjusted scheduling required for the new system. The consultant uploads the modified documentation to the client portal, allowing the client to view the scope adjustment. This step helps keep subsequent client records aligned with the revised project scope.

04

Adjusting Project Tasks and Scheduling

With the new proposal authorized, the firm updates the active project structure. Administrators modify the scheduling module to allocate extra hours for the consultant and create new tasks dedicated to the added system. This links the new technical requirements directly to the operational calendar, helping administrators keep project files and ongoing conversations organized without overlapping into adjacent client engagements.

05

Executing the Revised Invoice

After the security team completes the expanded assessment tasks, the engagement lead uses proposal-to-invoice conversion to generate the final invoices. The operator reviews the updated client records, modified Proposals, and completed tasks to compile the billing details. This process helps verify that the invoice accurately reflects both the baseline assessment and the newly authorized systems, avoiding unbilled consulting hours and providing transparency through the client portal for the final review.

Product coverage

Client operations for cybersecurity consultants

  • A person must check that an updated proposal can be generated and linked to an existing client record within three minutes of a scope change notification.
  • The human tester must verify that scheduling changes for the additional system are visible in the task module without deleting the original project timeline.
  • The operator must confirm that the final invoice successfully combines the original proposal amount and the new system assessment fee into a single itemized document.
Client records
Proposals
Projects and tasks
Files
Conversations
Scheduling
Invoices
Client portal
Workflow Automations

Loved on the App Store

Rated by the people running their client work on it.

★★★★★
Finally feels calm

Bounced between three or four all-in-one tools and always ended up in a mess of tabs. This is the first one that feels calm. Set up my client projects in ten minutes.

Justin R. · Solo founder · App Store review
★★★★★
Painless team rollout

Rolled it out to our eight-person team and adoption was painless — intuitive and polished. I'd love more integrations, but they keep shipping.

Samantha D. · Operations lead · App Store review
★★★★★
Hours back every week

Was juggling separate tools for notes, tasks, docs, and updates. Consolidating into one place has genuinely saved me hours each week. Support is responsive too.

Alicia N. · Agency founder · App Store review

Get started

See Workspace369 on your own client work.

Start a free trial or talk to sales — either way, you will see the whole loop: inbox, projects, portal, and billing.

FAQ

Evaluation Criteria for Scope Adjustments

How do we handle technical vulnerability data in Workspace369?

Keep vulnerabilities, credentials, security evidence and scanning in your approved security systems. Workspace369 holds the engagement record: note in the brief that a new system was added, and use files and conversations to track the business agreements, schedules and invoices.

Can we update project tasks when a security assessment adds a new system?

Yes. When a security assessment adds a new system after authorization and scope are agreed, an operator can configure workflow automations to handle task creation and adjust the scheduling module. This ensures the project timeline matches the technical work after proper configuration and testing.

How do clients review scope changes and updated billing?

Clients can access the client portal to review revised Proposals, updated scheduling, and final invoices. A person must test the required access to ensure the client can view these files and conversations, confirming that the scope adjustments are fully visible before processing the final payment.

Can Workspace369 automatically assign tasks to security engineers?

Workflow Automations can create tasks, send email or SMS, issue reminders and notify team members using supported triggers, conditions and timed waits. Email automations start at Cadet and SMS steps at Voyager; AI-drafted workflows start at Commander. Test the required event, owner and review step before enabling the workflow. Call triggers start on Specialist, where voice is included.

Ready when you are

See where Workspace369 fits into your client-work flow.

Start with the modules you need today, then turn on AI, automations, accounting, inventory, requests, and reporting as the operation grows.